
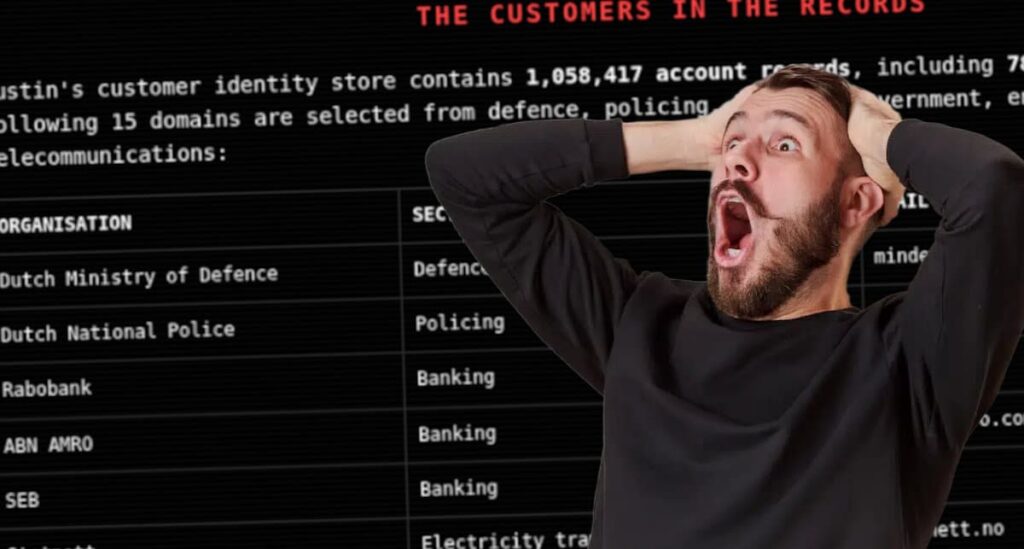
The leaked data is described as extensive. According to the hackers, it includes 24.5 million lines of source code for Dustin's web shops and customer portals, as well as a customer register with just over one million accounts. Among the exposed accounts are representatives from European actors within the police, banking, public administration and energy sectors.
In addition to customer data, the leak is said to contain over half a million internal cases from the Jira platform. The group highlights an internal case from 2022 where Dustin's security team allegedly warned of a lack of GDPR compliance regarding personal data in test environments. Furthermore, the stolen material includes excerpts from support cases containing 92 unique Swedish social security numbers in plain text, as well as financial information in the form of bank details and IBAN numbers.
Although the ransom demand was not paid, Fulcrumsec states that they have chosen to withhold specific contact details belonging to individuals within the police, banking and healthcare sectors in order not to unnecessarily expose these individuals to further risks.
Experts advise against downloading the files, as they may contain malicious code.
ALSO READ: Closed e-commerce for a week – now Dustin.se is back up again